 Coach
A request signature is a message authentication code computed by the client over a request’s parameters with a secret shared with the venue (typically HMAC-SHA-256 of the query string and body, sent in hexadecimal with the API key), which lets the venue check that the request comes from the key’s owner and was not altered; a timestamp and a validity window inside the signed payload stop old requests from being replayed.
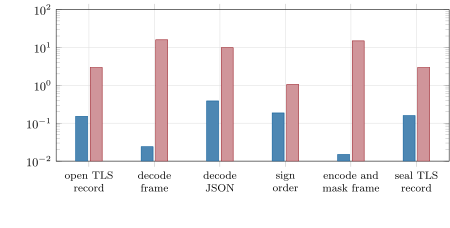
ssl (its record cost estimated as a quarter of the extra round-trip time over TLS). Measured on a laptop (Intel Core Ultra 7 155H) under WSL2, no isolated cores. Data: bench_web.py.